Notesfrom the workbench
Technical write-ups from our reverse engineering and security work, the same depth we bring to a matter.
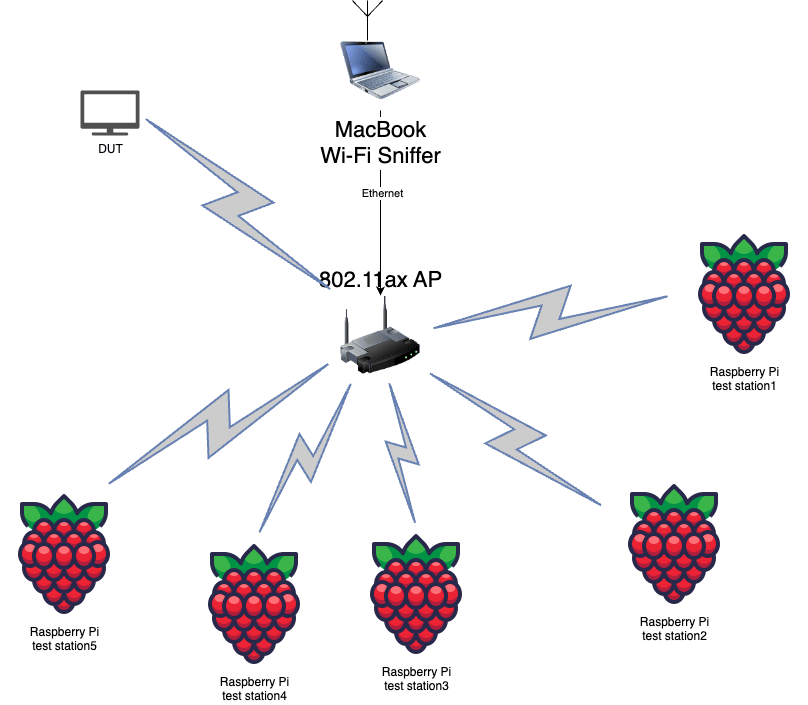
Triggering and Capturing OFDMA in Wi-Fi 6
What OFDMA is, how it applies to Wi-Fi, how to trigger it, and how to capture it.
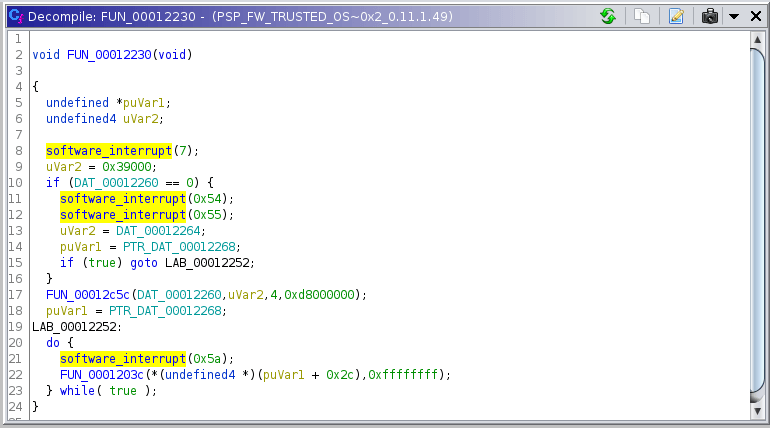
Resolving ARM Syscalls in Ghidra
With a simple script, you can have the Ghidra decompiler recognize syscall invocations as function calls.
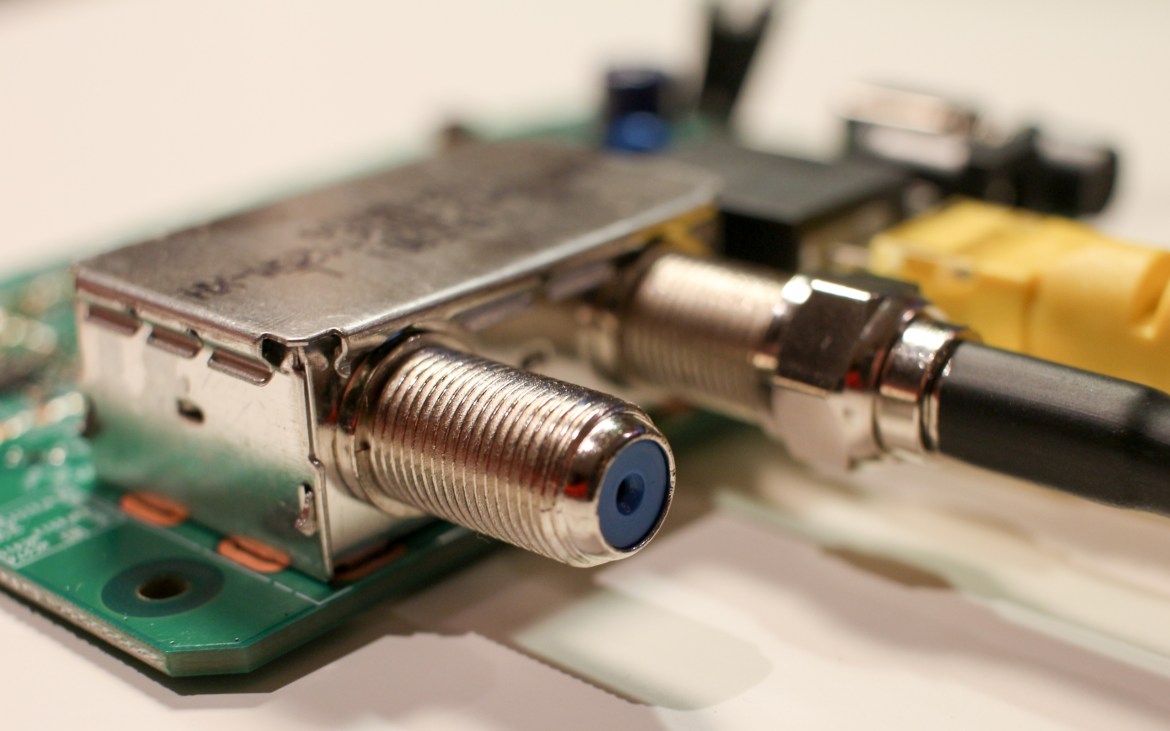
Hacking MoCA Like It’s 1999
Probing and reverse engineering a MoCA coax-networking stack, from the boot console to the protocol.
Android Device Hardening
Practical steps, and common pitfalls, in hardening Android-based embedded devices against tampering.
Securing Your Product
How to think about protecting the software and firmware inside the products you ship.
Hacking a Hardware Wallet
Writing custom firmware for a Trezor One hardware wallet, from build setup to running Pong on the device.
Machine Emulation with Ghidra
Using Ghidra’s emulator to execute and analyze firmware without the original hardware.
More on our external writing and conference talks.